Acme Corp, behind Cloud Workload Security
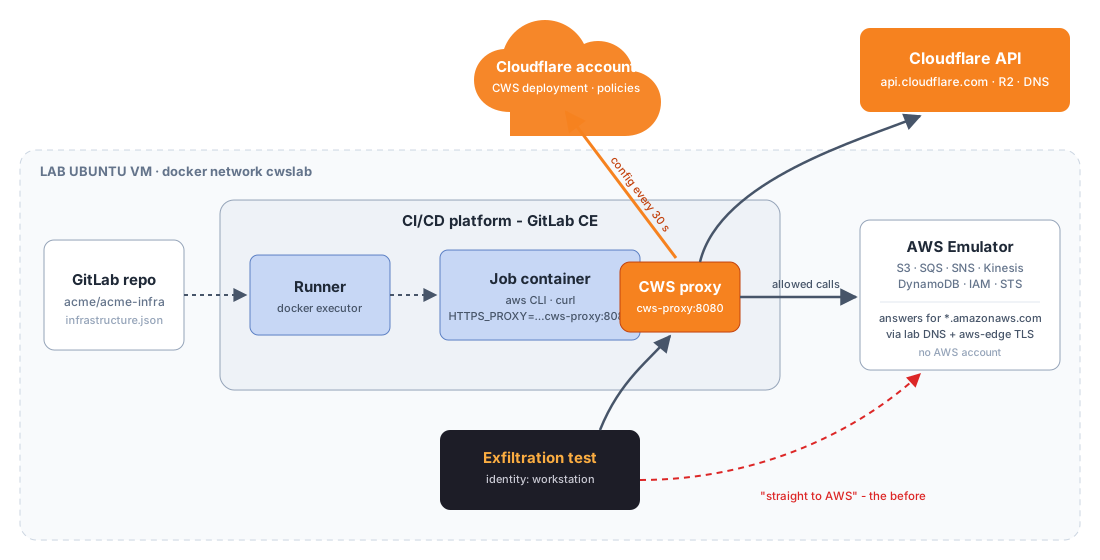
A fictional company with a CI/CD pipeline that deploys to AWS and to Cloudflare, a workload that can leak data through cloud APIs, and Cloudflare Cloud Workload Security in the path of every API call they make - all in one lab, with no AWS account.
Cloud Workload Security (CWS) puts a policy check between your workloads and the cloud APIs they call. A proxy you run in your own environment loads its policies from Cloudflare, reads each API request - the operation and its parameters, not just the hostname - and blocks the risky ones before they reach the cloud provider. It is Cloudflare's productisation of Kivera, acquired in 2024.
Cloud Workload Security in 20 minutes - the exfiltration test, a pipeline stopped mid-deploy on AWS and Cloudflare, and the evidence.
Setup first, though: it has this lab's credentials and a two-minute pre-flight check.
What is in the lab
| What it is | Reached as | |
|---|---|---|
| Exfiltration test | The Kivera data exfiltration test, rebuilt for Cloudflare - straight to AWS or through CWS, one click each | |
| Git server | GitLab and its runner, with the acme/acme-infra repository and its pipeline. GitLab on a VM with 8 GB or more, Gitea on a smaller one. | |
| CWS proxy | cws-proxy from Cloudflare's package repository, on the lab network | http://cws-proxy:8080, inside the lab |
| AWS | The AWS Emulator, answering for the real *.amazonaws.com hostnames | Inside the lab only |
| Cloudflare | This lab's own account: the CWS deployment and policies, R2, DNS, the tunnel and Access | dash.cloudflare.com |
| This guide | Scripts for every demo, and this lab's credentials | |
This guide is public. The exfiltration test and the git server are behind Cloudflare Access: sign in with a one-time PIN.
How it fits together
8 demos
Stop exfiltration
Five writes of company data to an attacker's S3, SQS, SNS, Kinesis and DynamoDB. All land; then none do. Chapter 1
Guard the pipeline
A one-line change would make a bucket public, leave a queue unencrypted, or hand out admin. Chapters 2 and 3
Guard Cloudflare too
A public R2 bucket and an exposed origin, blocked by the same proxy. Chapter 4
Run it for real
Monitor before enforcing, policy as data and code, identities, and the record of every decision. Chapters 5 to 8